PHP Version Upgrade Services
- Upgrade PHP 5.6, 7.x, 8.0 and 8.1 to PHP 8.4 or 8.5
- Replace removed functions like mysql_*, ereg_* and create_function()
- Update Composer dependencies and PHP extensions
Need to act on PHP2Shell fast? Legacyleap assesses your PHP estate and moves each application onto a supported runtime 50–70% faster, through governed code transformation, testing, and validation.
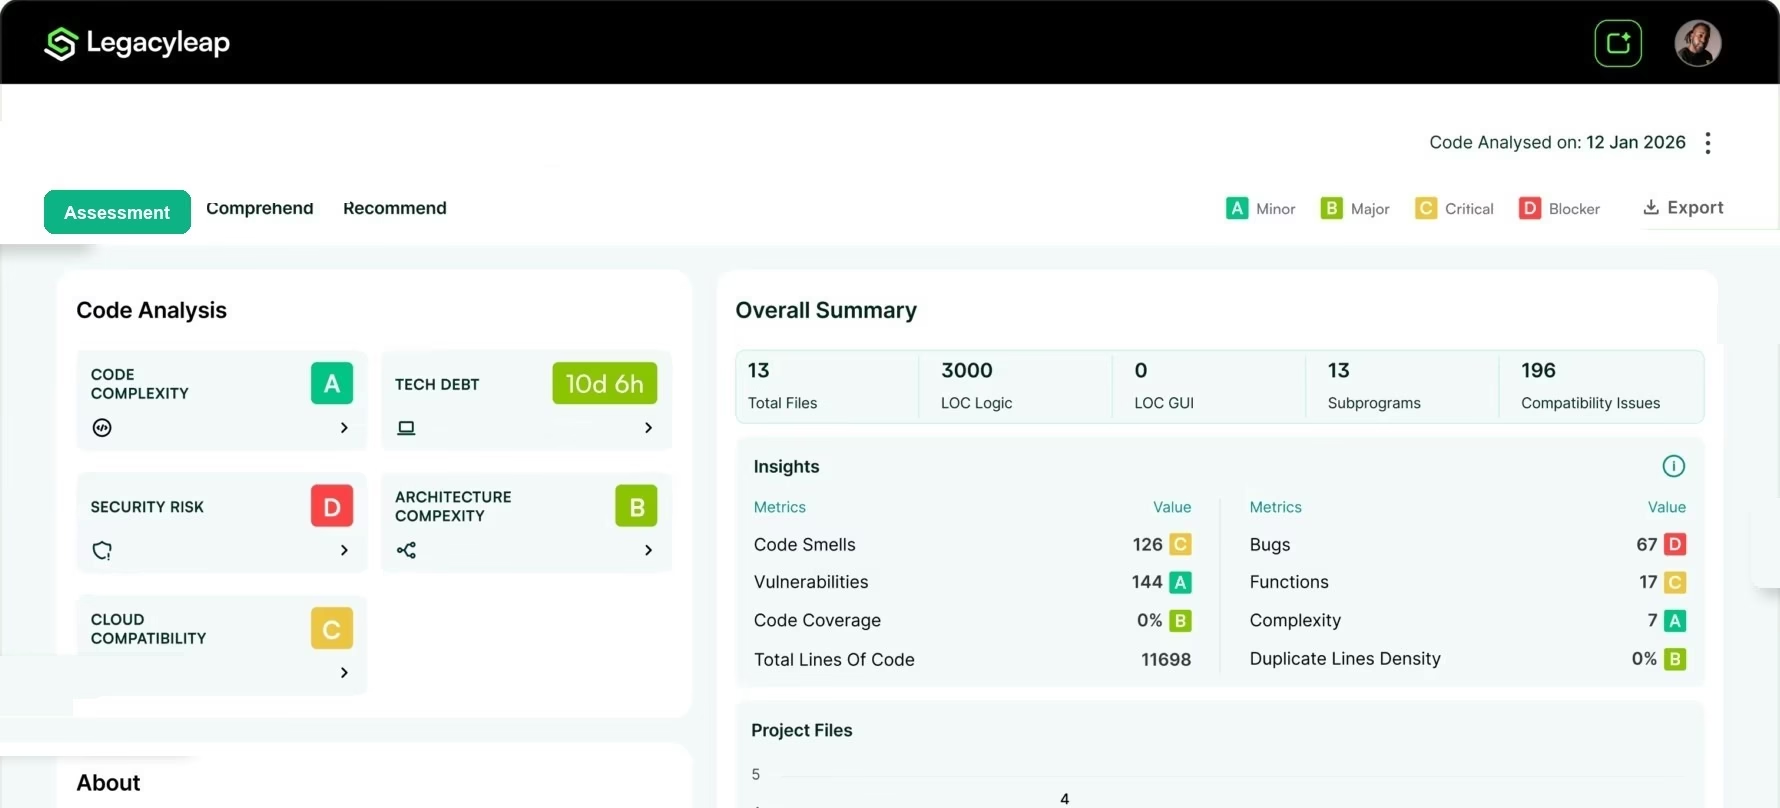 Legacy_PHP_Code
Trusted by enterprise engineering teams
Two critical PHP vulnerabilities went public in October 2026. Here is what it means for your applications and the steps to take now.
On October 21, 2026, researchers disclosed PHP2Shell, two critical flaws in the PHP engine (CVE-2026-109618 and CVE-2026-109619). With no login, attackers can run code on your server or steal passwords and API keys from its memory. The flaw lives in PHP itself, not your application, so updating your framework won’t fix it.
Find the version your applications run on to see whether it still gets security fixes, whether PHP2Shell is patched, and what to do next.
| PHP Version | Security Support | PHP2Shell Fix | What to Do |
|---|---|---|---|
| 8.3, 8.4, 8.5 | Supported | Fixed in 8.3.36, 8.4.27 and 8.5.12 | Update to the fixed release, restart every PHP process, and keep upgrading on your normal cycle |
| 8.2 | Ends December 31, 2026 | Fixed in 8.2.35 | Patch now, then upgrade to 8.4 or 8.5 before support ends |
| 7.4, 8.0, 8.1 | End of life | No official release, only source backports for teams that compile PHP themselves | Upgrade PHP and your framework together, or migrate to Java or .NET if the framework has no supported upgrade path |
| 5.4 to 7.3 | End of life | No fix from the PHP project | Plan a larger upgrade or a migration to Java or .NET, since jumping from PHP 5 or early PHP 7 brings the most breaking changes |
Versions older than PHP 5.4 have had no security support for more than a decade.
Our free Security Posture Assessment maps every legacy PHP application, flags the CVEs that can’t be patched, and recommends a migration path for each.
Whether you need a PHP version upgrade, a Laravel, CodeIgniter or Symfony upgrade, or a PHP to Java or .NET migration with a React or Angular frontend, Legacyleap’s PHP modernization services get your applications off unsupported PHP.
Legacyleap’s PHP migration services move applications off unsupported PHP versions in one of two ways: upgrade PHP and your framework, or migrate the application to Java or .NET.
Upgrade PHP to 8.4 or 8.5 and bring your framework with it, including Laravel version upgrades, CodeIgniter 3 to 4 migrations and Symfony upgrades.
What Changes
What Stays the Same
Rearchitect the backend onto Java 25 or .NET 10 and rebuild the frontend in React or Angular, carrying every business rule across.
What Changes
What Stays the Same
How to Choose
Choose the upgrade when the application is healthy and your team knows PHP. Choose a migration to Java or .NET when the framework has no supported upgrade path, hiring PHP developers is hard, or the architecture holds back new work. If you’re not sure, the $0 Modernization Assessment recommends a path for each application.
Applications on unsupported PHP need to reach a supported version quickly, working exactly as they did before. Legacyleap pairs AI agents with modernization engineers, backed by human review, parity testing and a full audit trail.
The Assessment Agent inventories every PHP application, version, framework, extension and Composer dependency, and flags the ones running on unsupported PHP.
The Documentation Agent maps routes, business rules, data flows and integrations, so the logic buried in old code is written down before anything changes.
The Recommendation Agent recommends upgrade or migration for each application, with ordered phases and effort and risk scored module by module.
The Modernization Agent combines deterministic upgrade tooling with AI and delivers every change as a reviewable pull request with a gap report.
The QA Agent replays real inputs against the old and new application, compares the outputs to prove they match, and packages the results into an evidence pack that shows production equivalence.
Tooling and agents automate the bulk of the conversion, so your engineers spend their time reviewing changes instead of rewriting code.
Every release ships with an evidence pack of repeatable tests and checksummed results that security, QA and compliance teams can verify for themselves.
Our modernization engineers review every agent change and resolve edge cases, and AI never merges or deploys code on its own.
The assessment and the migration run in your VPC or on-premise, using your approved AI models.
Trusted by enterprise engineering teams in healthcare, financial services, insurance, aviation and manufacturing
 Verified4.5/5
“Legacyleap’s deep expertise in older technologies de-risked critical knowledge gaps.”
Legacyleap was well versed in older technologies and frameworks that many newer developers weren’t familiar with.
 Verified5/5
“Legacyleap moved us from Desktop to Web without stopping the business.”
The team modernized with 95% less in-house effort, and discovered bugs users had experienced but never reported, along with unhandled corner cases.
After a flaw that leaks secrets from server memory, the last thing a security team wants is source code leaving the building. The assessment and the modernization both run inside your infrastructure.
Runs in your VPC or on-premise, inside your firewall.
Use your approved LLMs or self-hosted models, with no outbound API calls required.
Client code is never used to train models or shared across clients.
Every AI action is logged with role-based access and human approvals.
Find out which applications are exposed and where your security and compliance risk sits. Findings arrive in 3–5 days, and the report is yours whether or not you continue with us.
 Oct 23, 2026PHP 8.1 End of Life: PHP2Shell Patch Guide for Every VersionRead the article
 Feb 16, 2026PHP Migration Guide: Upgrade or Rearchitect Unsupported PHPRead the article
 Jun 16, 2026What Anthropic’s Claude Mythos Reveals About Legacy SecurityRead the article
 Apr 22, 2026Cyber Insurance Requirements: Legacy Systems in 2026Read the article
 May 7, 2026Legacy Software Compliance Risk: The 2026 Enforcement GuideRead the article
 Jun 24, 2026SEC Cybersecurity Disclosure Rules for Legacy System RiskRead the article
Yes. PHP 8.1 reached end of life on December 31, 2025, so it received no official release for PHP2Shell. The PHP security team published minimal source backports, which only help teams that compile PHP themselves.
Until December 31, 2026. PHP2Shell is fixed in 8.2.35, and after that date 8.2 receives no further security fixes, so teams on 8.2 should plan an upgrade to 8.4 or 8.5 now.
No. The flaw is in the PHP runtime, so the fix is a patched PHP release followed by a restart of every PHP worker and replacement of running containers. Framework updates leave the runtime as it was.
No. WAF rules block known exploit vectors for traffic that passes through the WAF. Requests that reach the origin server directly bypass it, and researchers track further variants, so treat a WAF as time to plan the move to a supported runtime.
It depends on the application. A healthy codebase with a team that knows PHP usually upgrades. A framework with no supported upgrade path, a custom codebase on PHP 5 or difficulty hiring PHP developers usually points to migrating to Java or .NET. The $0 Modernization Assessment recommends a path for each application.
Yes. The upgrade path keeps your application in PHP and moves the runtime and framework to supported releases together.
Legacyleap handles the step after the emergency: assessing exposure across your estate and moving each application onto a supported runtime. Server patching, threat hunting and breach investigation belong with your security or incident response team.
Assessment findings arrive in 3–5 days. Migration timelines depend on codebase size, framework and test coverage, and the $0 Modernization Assessment gives you an estimate for each application.
Share your stack details and get a map of your exposed PHP applications, the CVEs that can’t be patched and your compliance risk, in 3–5 days, inside your own infrastructure.
Book a $0 Security Posture Assessment
Find out which applications are exposed and where your security and compliance risk sits. Findings arrive in 3–5 days, and the report is yours whether or not you continue with us.